Somebody on your team used AI today. Probably more than once.
Maybe they cleaned up an email in ChatGPT. Maybe they dropped a 40-page PDF into a free chatbot and asked for the short version. Did they check with IT first? Nope. And honestly, why would they? It took a minute and saved them an hour.
That’s shadow AI. It’s mostly harmless right up until the file has client names in it, or bank info, or a patient chart. Then your data’s sitting on some vendor’s server and you’ve got zero say in what happens next. We’re not going to tell you to ban AI (it doesn’t work anyway). What works is figuring out what’s actually running, putting a few rules on paper, and giving your people approved tools they’ll actually want to use.
Key Takeaways
- Shadow AI is any AI tool your team uses that IT never signed off on.
- In IBM’s 2026 Cost of a Data Breach Report, 43% of breached organizations had a shadow AI incident. Last year? 20%.
- The big worries are leaked data, compliance fines, and AI agents doing stuff on their own.
- Banning it mostly just pushes it underground.
- If you’re in healthcare, finance, or accounting, pay extra attention.
Not sure what’s running on your network? Our managed IT security team can dig in and find out.
What Is Shadow AI?
Short version: it’s any AI tool someone uses for work without IT or security giving it the okay. It’s really a branch of shadow IT, the old name for apps and devices nobody approved.
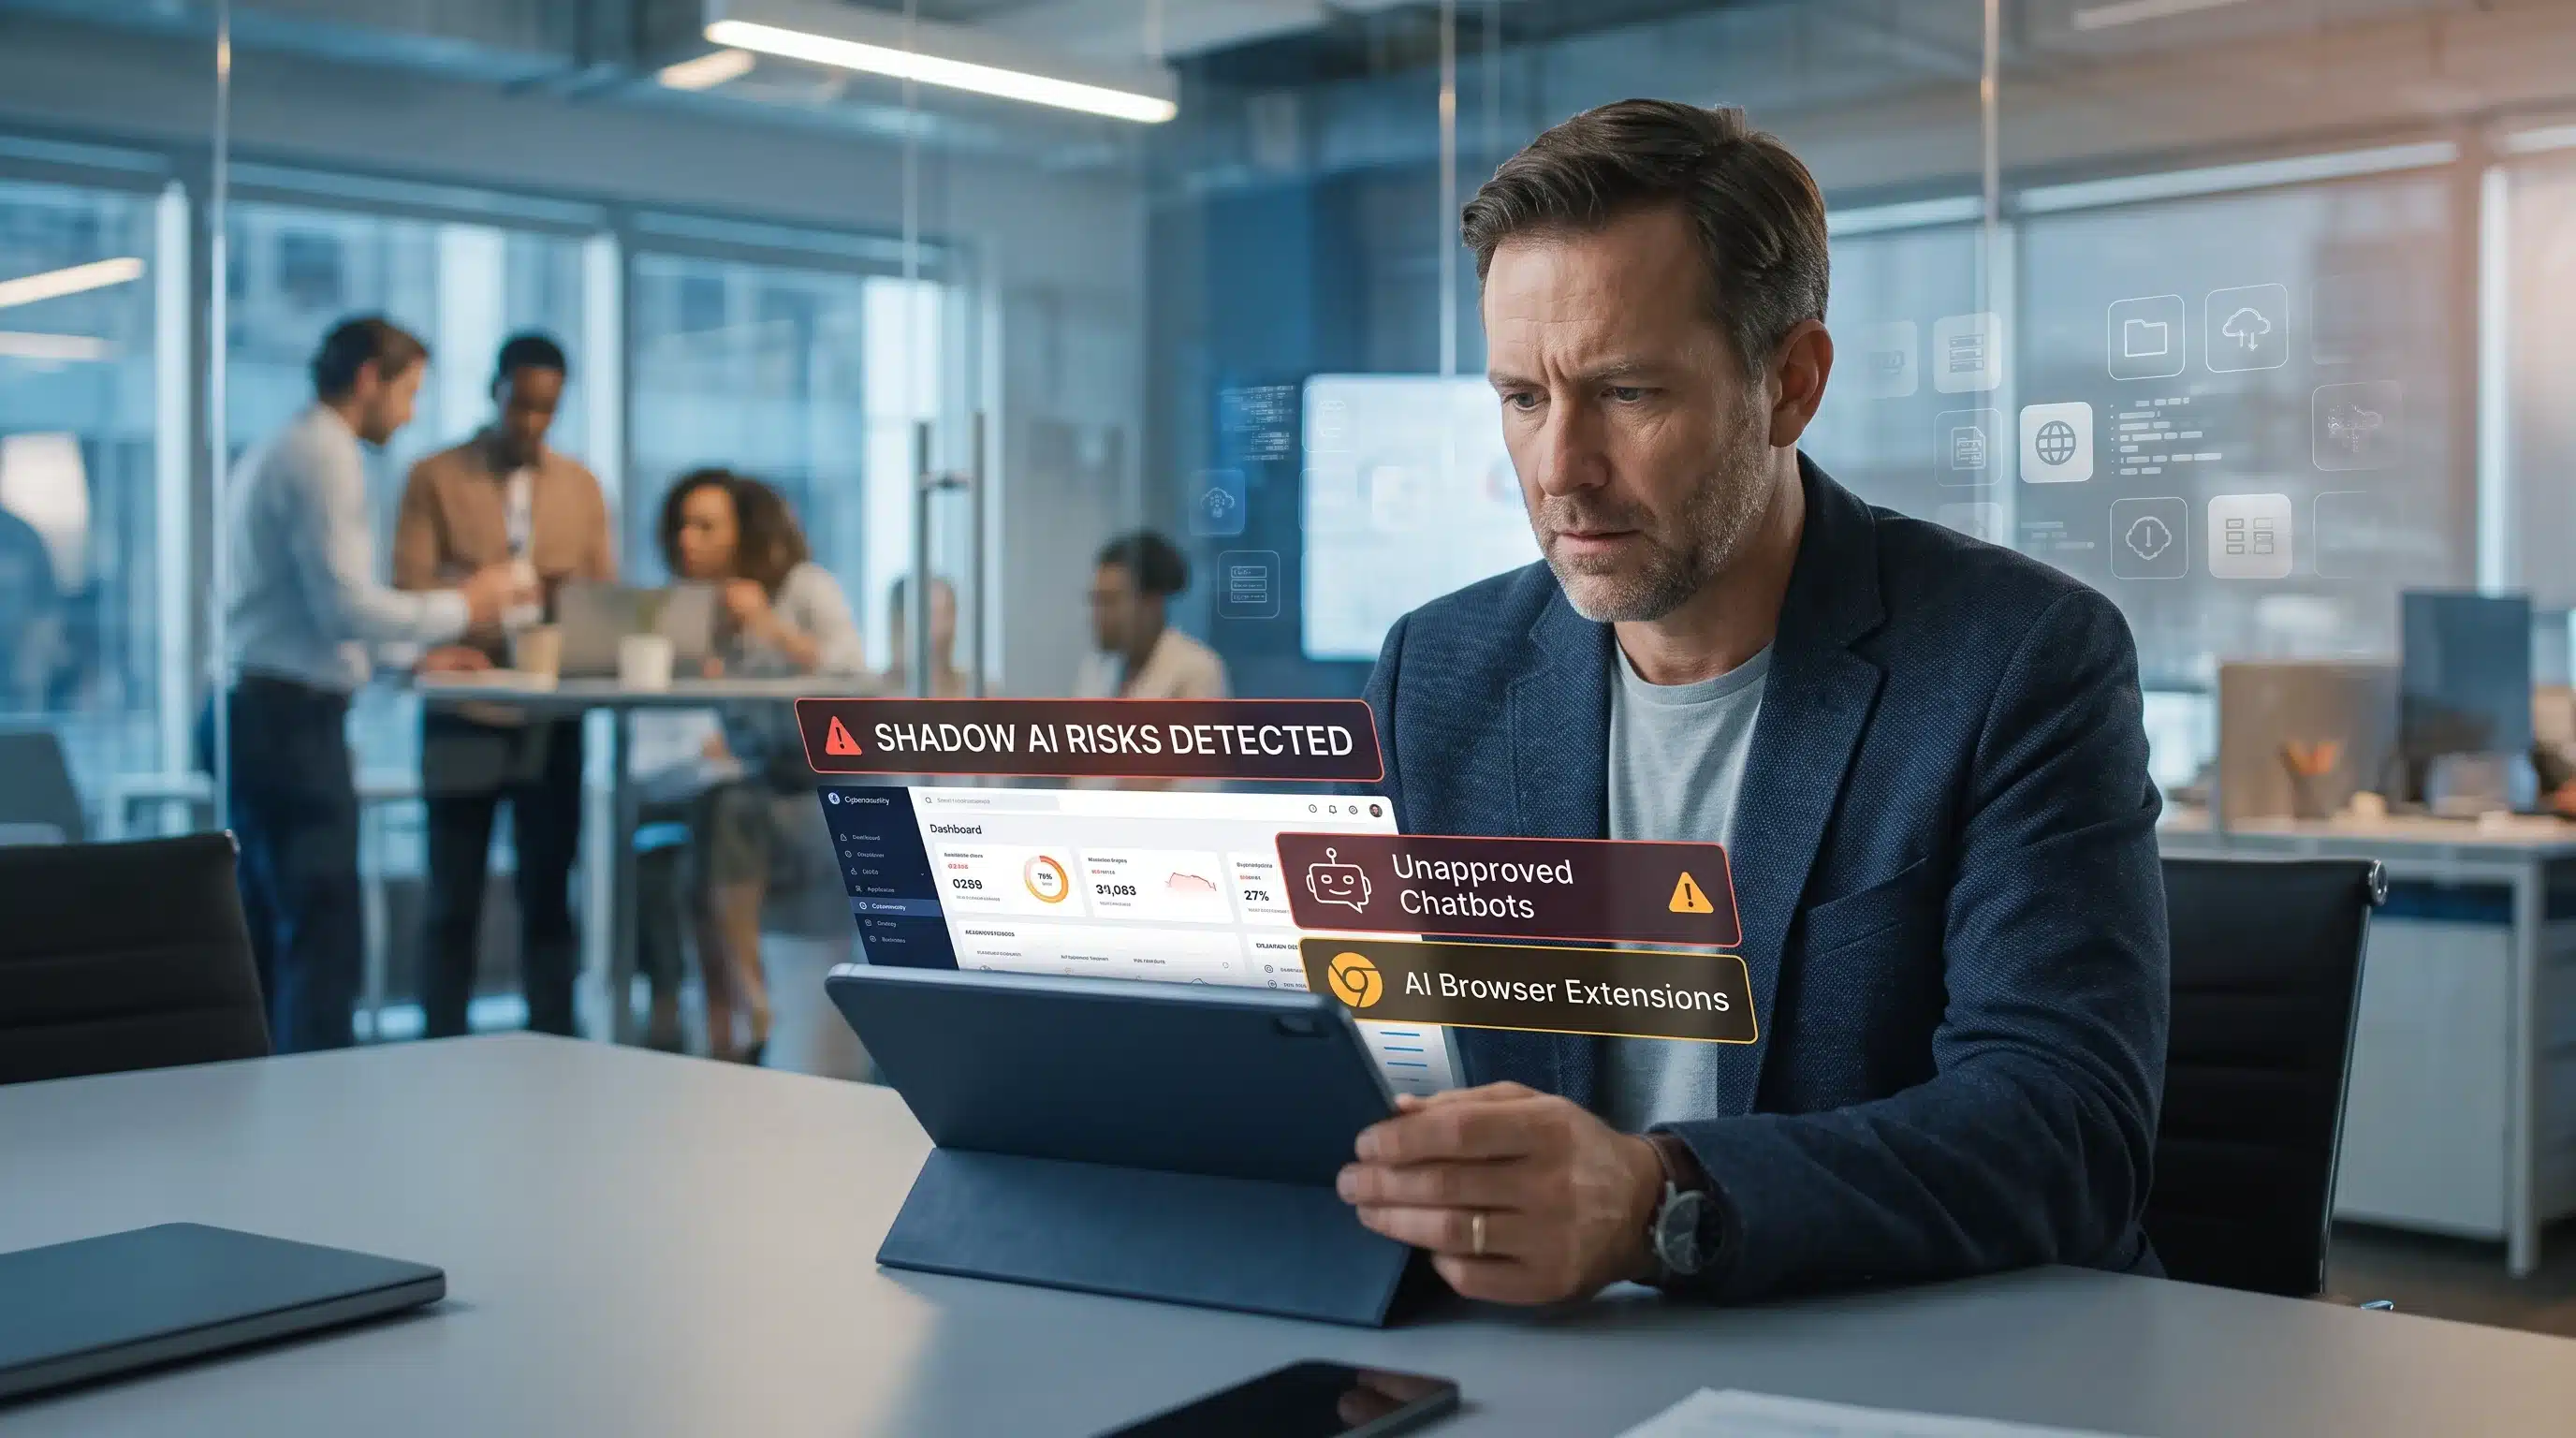
Here’s what it looks like in real life. Your bookkeeper uploads a client’s P&L to a free chatbot to double-check the math. A sales manager installs Otter so every Zoom call gets transcribed, and now those recordings live on someone else’s cloud. A project lead signs up for an AI writing app with a personal Gmail and connects it to the shared drive, because why not.
Nobody’s being shady. They’re just trying to get through their to-do list. But each one moved company data somewhere you can’t see, can’t audit, and can’t delete from.
Where it usually hides:
- Free chatbot accounts tied to personal emails
- Browser extensions that can read every page someone opens
- Meeting bots that record and store your calls
- AI features someone switched on inside apps you already pay for
- AI agents hooked up to inboxes, calendars, or shared files
Why Shadow AI Risks Are Growing in 2026
People have been sneaking AI into their workday for a couple of years now. So what changed? The bill.
IBM says the average cost of a shadow AI incident hit $5.39 million this year. In 2025 it was $4.63 million.
Fewer companies are paying attention, too. 68% of breached organizations had no AI governance at all, up from 63%. Only 29% regularly checked for unapproved AI tools, down from 34%. More AI. Less oversight. Bigger losses when something slips through.
The 5 Biggest Shadow AI Risks for Your Business
1. Client and Company Data Leaks
This is the big one. Someone pastes a contract or a pricing sheet into a public AI tool, and depending on the fine print, that vendor might store it, have a human look at it, or use it to train their next model.
You can’t take it back. And since IT never knew the tool existed, nobody knows the leak happened either. Not until it turns into a much bigger problem.
2. Compliance Violations and Fines
If you handle regulated data, you can fall out of compliance without anyone noticing. Medical offices have HIPAA to worry about. Accounting and financial firms have their own privacy and record-keeping rules.
And yes, the fines are real. About one in five shadow AI incidents ended in a regulatory fine.
3. AI Agents That Act on Their Own
Old-school chatbots just answered questions. AI agents actually do things. They send emails, move files, book meetings, update records, and sometimes nobody clicks “approve.”
Say an employee hooks an unvetted agent up to their Outlook. That agent now has every bit of access they do. One misread instruction, or a sneaky prompt hidden inside an incoming email, and it’s off doing things nobody asked for. Fast.
4. Security Blind Spots
Your firewall and endpoint tools can only protect what they can see. A random Chrome extension? A personal chatbot account on a work laptop? Mostly invisible.
Attackers love that. One compromised extension or stolen AI login, and they can see everything that tool ever touched.
5. Bad Decisions Based on Bad Output
AI gets things wrong. Confidently wrong. If someone trusts an unchecked answer for pricing, contract language, or client advice, that mistake goes straight into real work. Approved tools can have a review step. Shadow AI doesn’t have any steps at all.
Shadow AI vs. Shadow IT: What’s Different?
Shadow IT has been around forever. Think personal Dropbox, or a project app nobody approved. Annoying, sure, but it’s mostly a storage problem.
Shadow AI is a different animal:
- It works with your data. It reads it, summarizes it, rewrites it, and some tools keep a copy.
- It’s sneaky. Lots of AI features are tucked inside browsers and apps you already trust.
- It can act. An agent with the right permissions doesn’t wait for anybody.
That’s why blocking a few websites doesn’t cut it anymore.
How to Reduce Shadow AI Risks Without Banning AI
A blanket ban sounds great on paper. In real life? People keep using AI on their phones and home laptops, and now you can see even less. Better plan: give them safe options and keep an eye on things.
Take Inventory First
Just ask. Which AI tools are you using, and for what? Most folks will tell you if they don’t think they’re in trouble. Then have IT double-check browser extensions, connected apps, and traffic going out to AI services.
Write a Short AI Use Policy
Keep it simple. Your policy should cover:
- Which AI tools are approved
- What data never goes into one
- Who to ask before trying something new
One or two pages, tops. Nobody reads a 30-page policy.
Give People Approved Alternatives
If your team’s using a free chatbot because it saves time, fine. Give them a business version with real data protection, like Microsoft 365 Copilot or ChatGPT Enterprise. When the approved tool is also the easy tool, people follow the rules.
Lock Down Connections
Decide which AI tools get to connect to email, file storage, and your business apps. Nobody links an AI agent to a company account without sign-off. Most businesses can enforce this with identity and access tools they already pay for.
Train Your Team
Most shadow AI problems come from people who just didn’t know. Practical training fixes a lot of that: what’s okay to share, what isn’t, and what AI-powered scams look like. Our phishing awareness training covers all of it.
Keep Watching
New AI tools pop up every week, so a one-time audit goes stale in a few months. That’s where ongoing monitoring and active threat hunting come in. They catch new tools and weird activity early.
Which Businesses Have the Most at Stake?
Everybody using AI has some exposure. Some industries just have a lot more on the line.
- Healthcare: One patient record in the wrong chatbot can turn into a HIPAA headache. If your practice relies on healthcare IT services, treat AI tools like any other system that touches patient data.
- Finance and accounting: Tax returns, client financials, account numbers. None of it belongs in a public AI tool.
- Engineering, construction, and oil and gas: Bids and CAD drawings are your competitive edge. Letting an AI vendor hang onto them isn’t a great idea.
Frequently Asked Questions About Shadow AI
What is an example of shadow AI?
Classic one: an employee pastes a client contract into a free chatbot to get a quick summary. Meeting bots count too, the kind that record calls and store them on some outside server.
How do you detect shadow AI?
Start by asking your team. Then check browser extensions, connected apps, and network traffic to AI services. A managed IT provider can keep an eye on this all the time, so new tools get flagged in days instead of months.
How do you prevent shadow AI?
Make the approved option the easy option. Hand people a business-grade AI tool, write a short policy, and teach them what data stays off limits. Bans alone? They just push it out of sight.
What are effective controls for shadow AI usage?
An approved tool list is the starting point. Add access rules tied to each user, sign-off for any AI agent or integration, data loss prevention settings, and regular audits. Then train people so they know why the rules exist.
What are the best tools to deal with shadow AI?
Depends on your size and industry. Most businesses mix browser and endpoint monitoring, identity and access management, and data loss prevention. Smaller teams usually get more out of a managed IT provider that already runs all of that every day.
Get Backup on AI Security
AI can make your team a lot faster. You just need to know where it’s running and what it can reach.
That’s our thing. Elevated Technologies helps Houston businesses find hidden AI tools, set rules that make sense, and lock things down without slowing anybody down. Think of us as your IT superheroes, minus the capes. And with a 5-minute response time, you’re never left hanging when something looks off.
Want to see what’s running in your business? Give us a shout. Contact Elevated Technologies and talk to our team.